AI agents are becoming capable of doing much more than answering questions. They can retrieve information, use software tools, interact with APIs, analyze business data, and complete multi-step tasks with limited human intervention.
For businesses, this creates opportunities to automate workflows and improve productivity. However, it also introduces a critical question: how can organizations ensure that AI agents act within their authority, protect sensitive information, and make decisions that align with business policies?
This is where AI agent governance becomes essential.
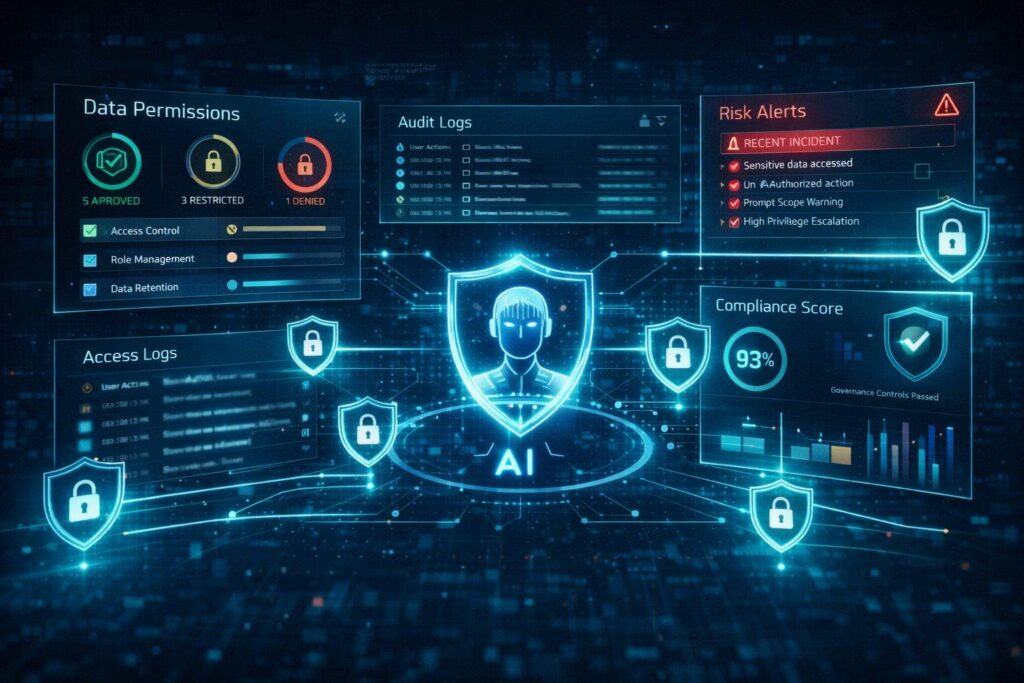
AI agent governance establishes the policies, technical controls, accountability mechanisms, and monitoring processes that determine how AI agents are developed, deployed, and operated. It helps organizations define what agents can access, which actions they can perform, when human approval is required, and how their behavior should be monitored.
As companies move toward more autonomous AI workflows, governance needs to become part of the system architecture rather than an afterthought.
In this guide, we explore AI agent governance, its key components, security risks, implementation framework, business benefits, and best practices for deploying AI agents responsibly.
What Is AI Agent Governance?
AI agent governance is the framework of policies, controls, responsibilities, and technical safeguards used to manage AI agents throughout their lifecycle.
Unlike a conventional chatbot that primarily generates responses, an AI agent may interact with external systems and perform actions. Depending on its permissions, it might create a support ticket, update a customer record, retrieve financial information, trigger a workflow, or modify files in a development environment.
These capabilities make governance especially important.
An AI agent should not automatically receive access to every tool or data source simply because it might be useful. Its permissions should reflect its purpose, the sensitivity of the information it handles, and the consequences of its actions.
A well-governed AI agent environment typically defines:
- Identity: Which agent is making a request?
- Authorization: Which resources and actions is the agent allowed to access?
- Policies: What rules must the agent follow?
- Human oversight: Which actions require review or approval?
- Monitoring: How are agent decisions, tool calls, and outcomes tracked?
- Accountability: Who is responsible when an agent produces an incorrect or harmful result?
AI agent governance combines organizational policy with enforceable technical controls. Written guidelines alone are insufficient if an agent can still execute unauthorized actions through connected tools.
Why Is AI Agent Governance Important?
The more autonomy an AI agent receives, the more important it becomes to control its access, actions, and operating environment.
An agent that only summarizes public documents has a different risk profile from one that can access customer records, issue refunds, change account permissions, or execute production commands.
Without appropriate governance, even a well-intentioned agent can make mistakes that affect customers, expose confidential data, or disrupt business operations.
Preventing unauthorized actions
AI agents may interact with systems that have real business consequences. Governance helps ensure that agents cannot perform actions outside their approved responsibilities.
For example, a customer service agent might be allowed to explain refund policies and prepare refund requests but require human approval before issuing a high-value refund.
Protecting sensitive business data
Agents often need context from databases, documents, APIs, or internal applications. Governance defines which information they can access and how that information may be used.
This helps reduce the risk of exposing confidential business information or retrieving personal data that is unnecessary for a task.
Improving transparency and accountability
When an AI agent takes an action, businesses should be able to understand what happened, which permissions were used, and whether the action followed established policies.
Useful records can help teams investigate incidents, troubleshoot unexpected behavior, and demonstrate compliance with internal requirements.
Supporting reliable business automation
Governance does not exist only to restrict agents. It also creates the conditions for deploying them with greater confidence.
When teams clearly define permissions, approval thresholds, escalation procedures, and monitoring requirements, they can automate appropriate tasks without granting unrestricted autonomy.
AI Agent Governance vs. Traditional AI Governance
Traditional AI governance often focuses on model performance, data quality, bias, explainability, and responsible use. These remain important for agentic systems, but AI agents introduce additional concerns because they can interact with tools and execute actions.
| Governance area | Traditional AI systems | AI agent systems |
|---|---|---|
| Main concern | Model outputs and decisions | Outputs, tool use, and actions |
| Access control | Access to model and data | Identity and permissions across connected tools |
| Risk management | Incorrect predictions or generated content | Incorrect outputs, unauthorized actions, and cascading workflow failures |
| Monitoring | Model performance and output quality | Tool calls, decisions, actions, and outcomes |
| Human oversight | Review of important outputs | Review or approval of consequential actions |
| Accountability | Model owner and business process owner | Clear responsibility across agent, tools, workflow, and business owner |
AI agent governance builds on established AI governance practices while extending them to cover the full action lifecycle.
Key Components of an AI Agent Governance Framework
An effective governance framework should cover the technical and organizational controls that keep agents operating within defined boundaries.
1. Agent Identity and Access Management
Every production AI agent should have a clearly defined identity and an associated set of permissions.
This makes it possible to distinguish one agent from another and determine which agent accessed a resource or initiated an action.
For example, an HR assistant that retrieves approved employee policies should not automatically inherit the permissions of an administrator or gain unrestricted access to payroll records.
Agent identities should be managed through appropriate authentication, authorization, credential management, and access review processes. Shared credentials and broad, permanent permissions make it harder to determine which agent performed an action and increase the consequences of a compromise.
2. Role-Based and Task-Based Permissions
AI agents should receive only the permissions required to complete their assigned tasks.
Role-based access control can define permissions according to an agent’s function. More granular policies can further restrict access based on the task, resource, user, environment, or risk level.
Consider an AI sales assistant. It might be allowed to read approved product information, summarize customer interactions, and draft follow-up emails. Sending messages, exporting customer lists, or changing account ownership may require additional authorization.
Permissions should be enforceable at the tool or application layer. An instruction telling an agent not to perform an action is not a substitute for preventing the action through access controls.
3. Policy Enforcement and Guardrails
Governance policies define which actions are allowed, restricted, or prohibited.
These rules may cover data access, external communications, spending limits, file modifications, customer commitments, and interactions with sensitive systems.
For example, a procurement agent might compare vendors and prepare a purchase recommendation while being prohibited from approving its own purchase request.
Policies should be translated into controls that can be checked before actions occur. Depending on the workflow, enforcement may involve authorization services, validation rules, transaction limits, or approval gates.
4. Human-in-the-Loop Approval
Not every AI-generated action needs human approval. However, actions with significant financial, legal, security, or customer impact often warrant stronger oversight.
A governance framework should distinguish between routine tasks that can be automated and consequential actions that require review.
A support agent might automatically categorize tickets and draft responses while escalating account closures or unusual refund requests to a human employee.
Approval workflows should also provide enough context for reviewers to make informed decisions. A simple approval button is less useful if the reviewer cannot see what the agent intends to do, which data it used, or what the consequences may be.
5. Monitoring, Logging, and Auditability
AI agent activity should be observable throughout the workflow.
Depending on the system’s risk level, logs may capture the agent identity, task identifier, tool calls, permission checks, approval decisions, execution results, and errors.
Sensitive information should be handled carefully when creating logs. Auditability should not become a reason to store unnecessary personal data, secrets, or confidential prompts indefinitely.
Monitoring should also identify suspicious patterns, such as repeated authorization failures, unexpected access attempts, unusually large data requests, or actions outside normal operating limits.
6. Risk Assessment and Lifecycle Management
Governance begins before deployment and continues throughout the agent’s lifecycle.
Organizations should assess the agent’s intended purpose, connected tools, data sensitivity, potential failure modes, and business impact. They should also review significant changes to the model, instructions, permissions, tools, or workflow.
An agent that was initially designed for internal document search may become riskier if it later gains access to customer databases or external messaging tools.
Periodic reviews help ensure that the governance framework remains appropriate as the agent’s capabilities and responsibilities evolve.
Common AI Agent Security Risks
AI agent governance must address risks associated with both AI behavior and the software environment in which agents operate.
Prompt injection
Prompt injection occurs when malicious or untrusted content attempts to influence an AI system’s behavior. This content might appear in a document, email, webpage, support ticket, or retrieved record.
An agent that reads a malicious email and has access to internal tools could be manipulated into attempting an unauthorized action.
Mitigations include treating external content as untrusted, limiting tool permissions, separating data from trusted instructions, validating actions outside the model, and requiring approval for sensitive operations.
Excessive permissions
An agent with unnecessary permissions can cause greater damage when it makes a mistake or is manipulated.
A reporting agent may need read-only access to selected records, not permission to delete data, change account settings, or modify production systems.
Regular permission reviews and narrowly scoped credentials help reduce this exposure.
Sensitive data leakage
Agents may inadvertently disclose confidential information through generated responses, external tool calls, logs, or connected applications.
Organizations should classify sensitive data, limit retrieval to authorized sources, apply output checks where appropriate, and prevent credentials or secrets from entering model context unnecessarily.
Unsafe tool execution
An agent may generate a command, database query, or API request that is incorrect or potentially harmful.
Tool integrations should validate parameters, enforce permissions, restrict dangerous operations, and use isolated execution environments where appropriate. Critical changes should be tested or approved before execution.
Cascading failures in multi-agent systems
When multiple agents coordinate, one agent’s incorrect output may influence subsequent decisions. An error can spread across a workflow if downstream agents trust earlier results without verification.
Multi-agent architectures should define responsibility boundaries, validate important intermediate outputs, limit cross-agent permissions, and provide a way to stop or reverse harmful actions.
The OWASP GenAI Security Project’s Top 10 for Agentic Applications is a useful reference for identifying agent-specific threats and planning technical mitigations.
How to Design a Secure AI Agent Governance Architecture
Governance is most effective when implemented across the architecture rather than relying entirely on the model’s instructions.
A practical architecture can be organized into several layers.
Identity and authorization layer
This layer identifies each agent and determines whether it is allowed to access a resource or perform an action. It should integrate with existing identity systems where appropriate and support narrowly scoped permissions.
Orchestration layer
The orchestration layer manages task execution, workflow state, tool selection, and coordination between agents. It should enforce task boundaries and prevent an agent from bypassing required checks simply by selecting a different execution path.
Tool and integration layer
This layer connects agents to APIs, databases, business applications, and other services. Each integration should validate requests and enforce its own authorization requirements.
Policy and approval layer
A policy engine or equivalent enforcement mechanism evaluates whether proposed actions meet the organization’s rules. It can apply restrictions, transaction limits, approval requirements, and escalation logic.
Monitoring and audit layer
This layer records relevant events and monitors for unexpected behavior. It supports incident investigation, compliance reviews, and continuous improvement.
Human oversight layer
Employees and designated owners remain responsible for high-impact decisions, exception handling, and policy changes. They should have a clear way to pause an agent or revoke access when necessary.
These layers should work together. For instance, an AI agent may recommend issuing a refund, but the authorization layer checks whether the agent can initiate the transaction, the policy layer evaluates the amount, and the approval workflow determines whether a human must authorize it.
The agent’s generated response should never be the only mechanism deciding whether a sensitive operation is permitted.
How to Implement AI Agent Governance Step by Step
Organizations can establish governance incrementally, beginning with a limited use case and expanding controls as agents gain greater autonomy.
Step 1: Inventory your AI agents
Identify all agents in use, including experimental tools, internally developed agents, and agents embedded in third-party applications.
Record each agent’s purpose, owner, model or platform, connected tools, data access, and operating environment. An accurate inventory is the foundation for assessing risk.
Step 2: Classify agents by risk
Evaluate the possible consequences of incorrect or unauthorized actions.
A read-only knowledge assistant may present relatively limited operational risk, while an agent that can modify financial records or change access permissions requires more stringent controls.
Consider data sensitivity, level of autonomy, transaction impact, external exposure, and the difficulty of reversing actions.
Step 3: Define ownership and accountability
Every production agent should have an accountable business owner and a technical owner. Responsibilities should cover deployment approval, permissions, monitoring, incident response, and periodic review.
Teams should also establish who can approve changes to an agent’s scope or authorize high-impact actions.
Step 4: Set permissions and action boundaries
Grant agents only the access necessary for their assigned tasks. Separate read and write permissions wherever practical, use temporary or task-scoped access when supported, and restrict access to sensitive operations.
Define which actions are prohibited, which are permitted automatically, and which require approval.
Step 5: Integrate governance with development
Governance should be included in design reviews, testing, deployment, and maintenance.
Before an agent goes live, test its behavior under normal conditions, malformed inputs, malicious instructions, permission failures, and unexpected tool responses. Verify that the system rejects unauthorized actions even when the model recommends them.
Businesses building custom AI applications can explore CopyWing’s website development services for information about its development and AI integration capabilities.
Step 6: Establish monitoring and incident response
Define what events should be logged, which behaviors should trigger alerts, and who responds to incidents.
Teams should be able to disable an agent, revoke its credentials, stop a workflow, or roll back changes when necessary. Recovery procedures should be tested rather than assumed to work.
Step 7: Review and improve continuously
Review agent permissions, performance, incidents, and policy compliance on a regular schedule and after significant changes.
Use the findings to improve system prompts, integration controls, testing, permissions, and approval rules. Governance should evolve alongside the agent’s capabilities and business responsibilities.
AI Agent Governance Best Practices
A governance program becomes more effective when its policies are translated into everyday engineering and operational practices.
Apply least-privilege access. Give every agent only the minimum permissions required for its purpose, and review those permissions when its role changes.
Separate recommendations from execution. Where risk is high, let agents prepare proposed actions while a separate policy or approval mechanism determines whether they may proceed.
Validate actions outside the model. Enforce transaction limits, input validation, access rules, and other critical requirements in software controls rather than relying solely on natural-language instructions.
Protect credentials and sensitive data. Use appropriate secret management, restrict access to confidential records, and avoid placing unnecessary sensitive information in model context or logs.
Test adversarial scenarios. Evaluate how agents respond to prompt injection, misleading documents, unexpected API results, unauthorized requests, and tool failures.
Maintain audit trails. Record relevant actions and approval decisions so teams can reconstruct what happened without collecting more sensitive data than necessary.
Provide emergency controls. Establish a reliable way to suspend an agent, revoke access, and contain a malfunctioning workflow.
Assign clear ownership. Define who is accountable for the agent, its connected systems, and the business outcomes it can affect.
Benefits of AI Agent Governance for Businesses
Good governance helps organizations adopt agentic AI without treating every deployment as an uncontrolled experiment.
Reduced operational risk
Clear permissions, action boundaries, and approval rules reduce the likelihood that an agent will make unauthorized changes or perform tasks outside its intended role.
Better protection of business data
Data-access controls and monitoring help prevent agents from retrieving or disclosing information they do not need.
Greater trust in AI automation
Employees and stakeholders are more likely to trust an agent when its responsibilities are clear, its actions can be reviewed, and there is a reliable way to intervene.
More controlled scaling
A consistent governance framework makes it easier to evaluate new agents against established requirements instead of inventing a separate process for every deployment.
Improved accountability
Ownership, audit trails, and incident procedures help businesses understand how decisions were made and who is responsible for resolving problems.
Governance does not eliminate all AI risks. Its purpose is to identify, reduce, monitor, and manage those risks so that the organization can make informed decisions about where and how to use autonomous systems.
How to Measure AI Agent Governance Effectiveness
Organizations should evaluate governance through operational evidence, not merely by counting the number of policies they have written.
Useful measures include:
- Unauthorized action rate: How often agents attempt or complete actions outside their permitted scope.
- Policy enforcement rate: Whether required restrictions are consistently applied.
- Human approval compliance: Whether actions requiring approval receive it before execution.
- Security incident frequency: How often agent activity contributes to a security or operational incident.
- Time to contain incidents: How quickly the organization can suspend access and stop harmful activity.
- Audit coverage: Whether important agent actions can be reconstructed from available records.
- Permission review completion: Whether scheduled access reviews are completed and unnecessary permissions are removed.
- Task success rate: How often agents complete approved tasks correctly without unacceptable rework.
- False-positive rate: How often security controls block legitimate activity unnecessarily.
These measures should be interpreted in context. For example, a low incident count does not necessarily prove that an agent is secure if monitoring is incomplete or unauthorized attempts are not being detected.
Common Mistakes to Avoid in AI Agent Governance
One common mistake is relying on system prompts as the primary security boundary. Instructions can guide behavior, but they cannot replace access controls, validation, and enforcement at the application layer.
Another mistake is granting an agent broad access during development and forgetting to restrict it before production. Development convenience should not determine long-term permissions.
Organizations also sometimes introduce approval requirements without defining clear thresholds. If every action requires approval, workflows become inefficient; if no consequential actions require review, risk can increase. Approval policies should reflect the potential impact of each action.
A further mistake is treating governance as a one-time checklist. Agents change as models, prompts, integrations, tools, and business requirements evolve. Reviews and testing must continue after deployment.
Finally, businesses should avoid measuring success only by the number of tasks automated. A useful governance program balances automation with accuracy, security, recoverability, and business value.
The Future of AI Agent Governance
As AI agents become more integrated into business systems, governance is likely to place increasing emphasis on agent identity, fine-grained authorization, action-level monitoring, and coordination between multiple agents.
Organizations will need to understand not only which AI model is being used, but also which agent initiated a request, what authority it had, which tools it accessed, and what changes it made.
Security approaches that focus only on model behavior will not be sufficient for systems that can take actions through external applications. Governance will need to extend across models, orchestration systems, APIs, identity infrastructure, and business workflows.
Standards and practical security guidance are also evolving. NIST’s August 2026 guidance on the identity foundations of agentic AI highlights why identity and authorization are important as organizations deploy agents across connected systems.
The long-term direction is not necessarily to make every agent fully autonomous. It is to give each agent an appropriate level of autonomy based on its purpose, risk, and the controls surrounding it.
Conclusion
AI agent governance is a foundational requirement for organizations that want to deploy autonomous AI workflows responsibly. It brings together identity, permissions, policy enforcement, human oversight, monitoring, and accountability to ensure that agents operate within defined boundaries.
Businesses should begin by understanding which agents they have, what systems those agents can access, and what consequences their actions could create. From there, they can implement least-privilege access, independent action validation, risk-based approvals, audit trails, and continuous testing.
The goal is not to prevent AI agents from doing useful work. It is to make their work secure, observable, and accountable.
As agentic AI adoption expands, organizations that build governance into their architecture from the beginning will be better prepared to scale automation while maintaining control over their systems and data.
Frequently Asked Questions About AI Agent Governance
What is AI agent governance?
AI agent governance is the set of policies, technical safeguards, ownership responsibilities, and monitoring practices used to control how AI agents access data, use tools, make decisions, and execute actions.
Why is AI agent governance important?
It helps organizations manage risks related to unauthorized actions, data exposure, incorrect decisions, tool misuse, and multi-agent failures. It also supports accountability and more controlled adoption of AI automation.
What are the main components of AI agent governance?
Key components include agent identity, access control, policy enforcement, human approval, monitoring, auditability, risk assessment, and lifecycle management.
How is AI agent governance different from AI governance?
AI governance covers broader issues such as model risk, fairness, transparency, privacy, and responsible use. AI agent governance adds specific controls for tool access, agent permissions, autonomous actions, workflow execution, and action-level accountability.
How can businesses secure AI agents?
Businesses should apply least-privilege permissions, validate tool calls, protect credentials, test for prompt injection, monitor agent activity, require approval for high-impact actions, and maintain incident-response procedures.
Do all AI agent actions require human approval?
No. Low-risk, reversible tasks may be automated when appropriate controls are in place. Actions with significant financial, legal, security, or customer impact may require human approval based on the organization’s risk policy.
What is the biggest risk of autonomous AI agents?
There is no single biggest risk for every deployment. Common concerns include excessive permissions, prompt injection, sensitive data exposure, unsafe tool execution, and errors that spread across connected workflows. Risk depends on the agent’s capabilities and environment.
How should an organization start an AI agent governance program?
Start by inventorying existing agents, assessing their risks, assigning owners, limiting permissions, defining approval rules, and implementing monitoring. Pilot the controls on a specific use case before expanding the program.
Can AI agent governance improve business productivity?
Yes. Clear permissions and approval rules can make it easier to automate appropriate tasks while reducing uncertainty and operational risk. The objective is to enable safe automation, not to add unnecessary restrictions to every workflow.
How often should AI agent governance be reviewed?
Governance should be reviewed periodically and whenever there are significant changes to an agent’s model, tools, permissions, data access, or business responsibilities. High-risk agents may require more frequent reviews.